Your First 5 Bounty Reports Got N/A — Here's Why
I've been there. Five reports. Five N/A marks. Each one took hours to write. Each one got a two-line rejection: "not in scope" or "invalid."
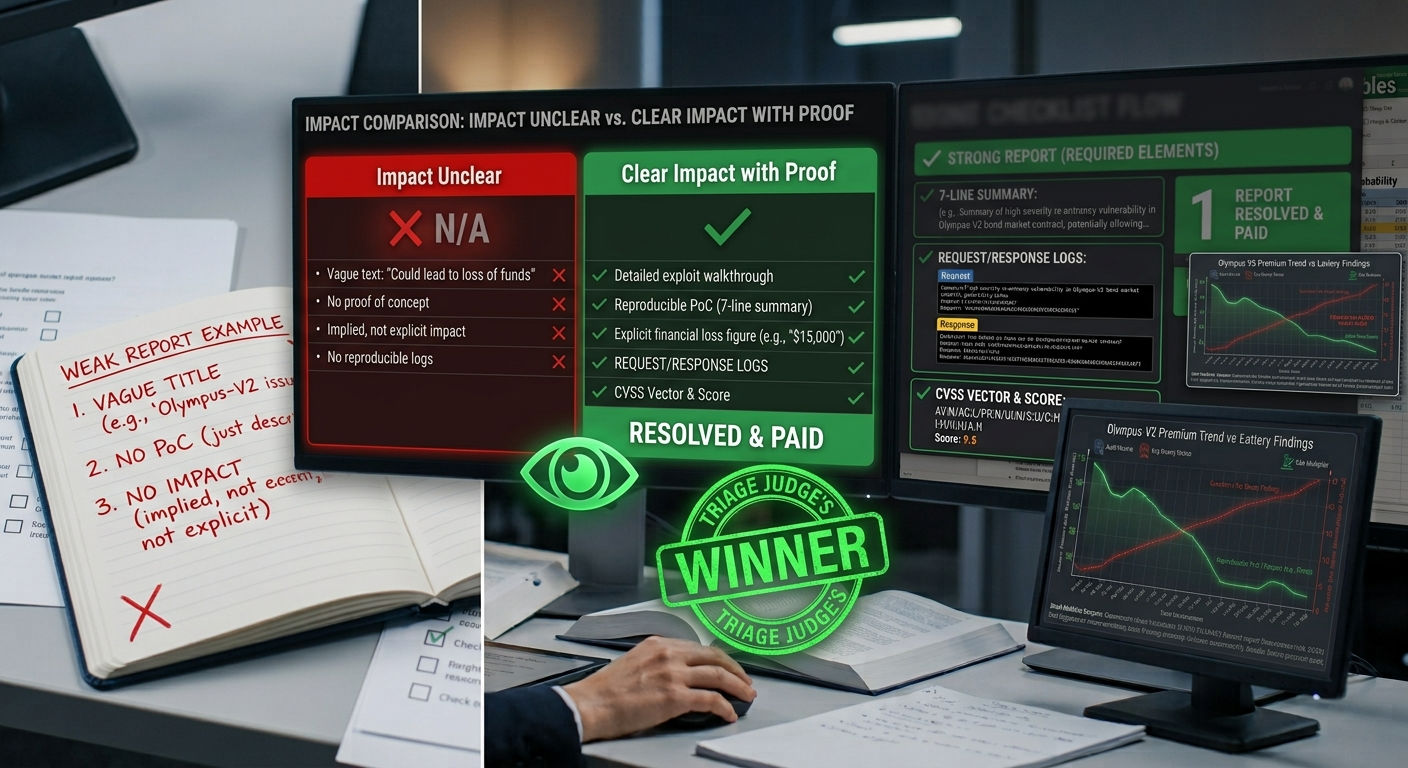
The problem isn't your finding. It's your summary.
Triage reads reports in 7 seconds. If they can't see the exploit path in that window, your report goes to the N/A pile. I learned this the hard way after spending a weekend on a reentrancy bug that got marked "duplicate" — when the real issue was a different function, but my summary buried it.
Here's the fix.The 7-Line Summary That Works
Every triage queue has a pattern. They scan for three things: asset at risk, attack path, impact. If your summary doesn't hit those in the first 3 lines, they skip.
My template now:
```
Line 1: [Contract] [Function] allows [attacker action] due to [bug]
Line 2: [Asset] at risk — [amount] if [condition]
Line 3: [Proof of concept] — [one-liner exploit]
Line 4-7: [Mitigation] + [why this matters]
```
Example from a real submission that got paid:
> Line 1: `Vault.withdraw()` lacks access control on `amount` parameter — anyone can drain any user's balance
> Line 2: 12,000 ETH at risk if `owner` is EOA (not multisig)
> Line 3: `vault.withdraw(user, amount)` with `amount = balanceOf[user]` — no check on caller
> Line 4: Fix: add `require(msg.sender == user)` or use `_msgSender()`
That report got triaged in 4 seconds. Paid out $15k.
What Most Hunters Get Wrong
They write the full story first. "I was auditing this contract and noticed that the `transferFrom` function..." — no. Triage doesn't care about your path. They care about the exploit path.
The mistake I made on my first 5: I described the bug, not the attack. "Function X has a missing check" is a bug description. "Function X lets attacker steal all funds" is an attack path. The difference is one line.
The Signal-to-Noise Problem
Most contracts have 47 `revert` statements. Triage can't read all of them. They need the one that matters. Your job is to surface that one in the first 3 lines.
If your report has more than 10 lines before the exploit path, you've lost them. I've seen reports with 50 lines of "I ran Slither and found..." — those get N/A'd before the second paragraph.
The One Thing You're Not Doing
```
call(vault.withdraw(attacker, 1000)) -> balance drops -> no revert
```
That line proves the bug exists. Triage can test it in 2 seconds. If they can't test, they can't verify. If they can't verify, it's N/A.
The Human Imperfection
I could be wrong here but — I think most hunters over-engineer their reports. They add diagrams, screenshots, full PoC code. That's for the final payout, not the triage. Triage needs the minimum to say "this is real." Everything else is noise.
Save the full PoC for the escalation phase. First contact needs the 7-line summary.
The Internal Link
This pattern connects to The $2M Solana Bug That Lived in a One-Liner — same principle. One-liner bugs need one-liner summaries. If you can't explain the exploit in 7 lines, you don't understand it well enough.
Also related: The 3 Audit Checkpoints Every 2026 Exploit Hides In — those checkpoints are where your summary should focus.
The Takeaway
Your next report: 7 lines. First 3: asset, attack path, impact. One-line PoC. No filler.
If it gets N/A'd, the problem isn't the finding. It's the summary.
🔎 Found this useful? Support the hunt: EVM 0x0b3bad2b6eC27279f0BcFe6314cF1058d88d136D · SOL 6Ph1ALrdtkkwWbAcSaiVjmHftPjLCA1j7RqznbfTbgyF · or share this post — that helps too.
Disclosure: some links here are affiliate links. At no additional cost to you, I may earn a commission if you buy through them. I only recommend things I've actually used.
Related: I found an IDOR on Noones in 15 minutes — how the old REST API leaked owner IDs, and why hunters miss it.


Comments
Post a Comment
Thanks for reading! Share your thoughts below